

The leading provider of crowdsourced cybersecurity solutions purpose-built to secure the digitally connected world...Unleash Ingenuity™
San Francisco, CA
Joined September 2012
- Tweets27K
- Following6.1K
- Followers207K
- Likes18.8K




Thank you for your time @kuzushi!
And we have another Hive Exchange event coming up!
Join us! 👇
luma.com/ko1b052l
www.teapawt.org/kuzushi/status/2121030…

ALT A vintage orange Volkswagen van is parked by a canal in a picturesque autumn setting with colorful trees and historic buildings, likely in Amsterdam. The sky is clear under a warm sunset. Prominent logos include AWS, Bugcrowd, and Just Eat Takeaway.com. Dominating the image is bold text: "Join Us.

Just got finished talking at the @bugcrowd hive event in Boston-- what a great time, thanks everyone for coming out.


UPCOMING EVENT: AWS and Just Eat Takeaway.com are joining us in Amsterdam for THE HIVE EXCHANGE.
Connect with infosec professionals and security researchers to explore how offensive security and hacker collaboration accelerate vulnerability detection and strengthen overall defense.
Connect, learn, and have fun!
📍 Amsterdam | 18 November
Request your spot 👇
luma.com/ko1b052l

We sat down with Dani Woolf to explore the parallels between chess and preemptive security. Check out the blog to learn how to keep attackers in check ♟️ bugcrowd.com/blog/checkmate-…

Nice work @NahamSec! 🔥
www.teapawt.org/NahamSec/status/211806…


Is that AI agent actually legit, or just another flashy demo?
Watch the on-demand webinar to learn more about evaluating AI testing agents:
event.on24.com/wcc/r/5473529…
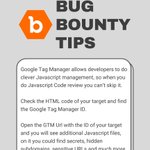
ASN enumeration is an important yet frequently overlooked recon method.
Finding the ASN can reveal the target's network ranges.
Tools include:
- asnlookup.com/
- bgp.he.net/
- @Yassineaboukir's ASNlookup
And more!
What tools do you like to use?


Don't hunt alone. Trade tips, swap PoCs, and level up with other researchers who get it. 👇

1
18
3,278
Join our community on Reddit 👇
reddit.com/r/Bugcrowd/
We're hiring! We have a bunch of great career opportunities available globally. Check them out on our careers page and join our awesome team. bugcrowd.com/about/careers/#…


T-Mobile just released its Advancing Cybersecurity at T-Mobile Report and it's a must-read! We're proud to play a part in helping T-Mobile on its preemptive security journey.
"Our Bug Bounty program, managed with Bugcrowd, remains one of the telecommunications industry's most impactful programs. To date, our Bug Bounty program has received over 1,400 valid submissions. As the program has matured, submissions have become increasingly sophisticated, reflecting stronger defenses and a higher barrier for potential attacks."
Read the full report here: t-mobile.com/news/_admin/upl…
📣 Calling all hardware hackers! 📣
If you're attending Hardwear.io in the Netherlands next week, be sure to find Bugcrowd customer Cisco, who will be handing out hardware for you to test as part of their HardPwn live hacking event. Find out more here: hardwear.io/nl-2026


When designing malware to evade modern Endpoint Detection and Response (EDR) solutions, red teamers must focus on 3 primary components:
🟧 pretexting the software
🟧 hiding the payload
🟧 executing the payload.
The critical 2nd step, hiding the payload, is the focus of this blog: 👇
bugcrowd.com/blog/weird-ways…
