

Official updates for developers building with @1Password. Securely manage API keys, credentials, and agent access without exposing your secrets.
Joined April 2026
- Tweets675
- Following228
- Followers1.5K
- Likes660



Developers lined up at Web Summit in to learn how to secure AI agents with @marianebekker , @alecksandruhh, @1Password.
That tells you where 2027 is headed.
1
102
Hackers are using always on agents to find your company’s secrets.
Microsoft caught one going from exposed GitHub credentials to stealing data from Azure Key Vault in just 5 MINUTES.
No need to manually hunt for secrets. Agents can do it at machine speed.
Your leaked API key is now a ticking clock.
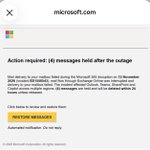
Hackers exploited a real Microsoft 365 outage to launch a massive phishing campaign.
The goal? Likely credential theft.
Fake Microsoft alerts told employees they had 24 hours to recover missing emails.
Here’s how the attack worked and 4 ways to protect your credentials. 🧵

3/ Why does this matter?
One stolen Microsoft 365 login could give attackers access to:
→ Corporate email
→ Teams conversations
→ SharePoint and OneDrive files
→ Internal phishing opportunities
And if sessions or tokens are compromised, changing a password alone may not be enough.
1
1
91
4/ Four ways to protect your credentials:
1. Use phishing-resistant MFA like passkeys or security keys.
2. Verify service alerts directly in the Microsoft 365 admin center.
3. Monitor suspicious logins, OAuth grants, and inbox rules.
4. If credentials were entered, reset them and revoke active sessions.
The lesson: a real outage can become the perfect phishing lure.
Source: microsoft.com/en-us/security…

1
79
1Password Developers retweeted
Congrats to @Cognition on the launch of Devin Bots.
When a Devin Bot spins up a team of agents for a weeks-long project, how are you keeping all those credentials secure?
1Password Developers retweeted
Upgrades, people. Upgrades. 🤝
Smarter agents → more tasks that need a secure login.
@1PasswordDev for AI and agents is coming to OpenAI dots as well, so they can sign in while your credentials stay secure:
www.teapawt.org/JamesZmSun/status/2122…


1Password Developers retweeted
What Mandiant's guidance recommends:
1. Lock down admin systems
2. Use short-lived credentials
3. Limit access
4. Segment networks
5. Watch for spikes in API and identity activity
For AI services: set budget alerts and scan your code for leaked keys.
🧵(9/10)

178 organizations. One compromised third-party platform.
Attackers exploited Optimizely to inject malicious JavaScript into websites including Zoom, CNN, BBC, and Salesforce.
The code could steal payment data, hijack crypto transactions, and target iPhones.
5 things developers can do to protect themselves 🧵

4. Protect credentials and sessions.
Use HttpOnly, Secure, and SameSite cookies. Avoid storing sensitive tokens in localStorage.
Give vendor integrations least-privilege access and require MFA for admin accounts.
Reduce what compromised JavaScript can steal.
1
2
230
