

Cloudflare is the world’s leading #ConnectivityCloud, and we have our eyes set on an ambitious goal — to help build a #BetterInternet.
300+ cities in 100+ countries
Joined April 2009
- Tweets48.5K
- Following5.4K
- Followers33K
- Likes6.3K




Java4Shell is a critical memory-corruption flaw in OpenJDK's Base64 decoder that can lead to remote code execution. Cloudflare has released six WAF managed rules for paid plans that logs matching requests by default. Patch your Java runtimes now. cfl.re/497qWXr

We literally painted San Francisco orange for #CloudflareConnect 🧡🏙️ Missed the action in SF—or want to relive the best moments? Watch all keynotes and breakout sessions on demand for free: cloudflare.com/connect/#sess…
Quad9's forced withdrawal from France highlights the dangers of mandating DNS-level blocking.
Read more: cfl.re/4f0cowv

Cloudflare retweeted

As part of the continued @Cloudflare solution set and practical advice for defense in depth strategies against vulns and emerging TTPs, we are introducing the Identity-Gated Edge architecture.
See link > developers.cloudflare.com/re… (HT @KennyJohnsonATX)

Region: Earth is taking over Vegas. Dec 1-3.
cloudflare.com/events/vegas/

A temporary WAF rule helps reduce risk, but it is not a substitute for fixing the underlying vulnerability.
Join Grant Bourzikas, Cloudflare’s CISO, and Daniele Molteni, Director of Product for Application Security, this Thursday, November 19th for practical guidance on checking exposure, verifying relevant managed rules are in Block mode, and prioritizing remediation.
Don't leave your runtime exposed—register now! cfl.re/4z6KDth

Join Grant Bourzikas, Cloudflare’s CISO, and Daniele Molteni, Director of Product for Application Security at Cloudflare, for a practical discussion grounded in the recent PHP2Shell vulnerabilities. They’ll cover how AI is changing attack and defense, and how teams can combine threat intelligence, WAF managed rules, and timely patching. cfl.re/4fCMe2T

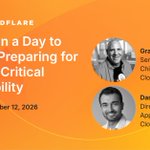
ALT A promotional image for a Cloudflare webinar titled "Less Than a Day to Defend: Preparing for the Next Critical Vulnerability" scheduled for Wednesday, December 9, 2026, at 10:00 AM PT. It features two speakers: Grant Bourzikas, Senior Vice President, Chief Security Office, and Daniele Molteni, Director of Product for Application Security. The Cloudflare logo is visible at the top.
Spend Management adds opt-in spending caps for Cloudflare Workers and Durable Objects, and more products soon. Here is how we built the metering pipeline that turns usage into runtime decisions. cfl.re/4iX4BRe

Kitesurf, our experimental browser engine for AI agents, is now open source. Inspect the code, run it locally, or deploy your own instance on Cloudflare Workers. cfl.re/4eHmAK6

AI-orchestrated penetration testing platforms like ARTEX have become increasingly powerful tools enabling effective attacks on exposed infrastructure. blog.cloudflare.com/adapting…

Observability matters. You cannot fix what you cannot see. What is the first metric you check when you suspect a system issue? #CloudflareChat
AI-assisted vulnerability discovery and exploit development are rapidly narrowing the time security teams have to respond.
Join Grant Bourzikas, Cloudflare’s CISO, and Daniele Molteni, Director of Product for Application Security, on November 19th for a practical discussion using the recent PHP2Shell disclosures as a case study. They’ll examine how teams can assess exposure, deploy WAF managed protections to buy time, and prioritise remediation.
Don't wait to assess your exposure—register now cfl.re/4z6KDth

We're excited to announce that Cloudflare is building an experimental consensus service using a never-before-deployed consensus algorithm, QuePaxa. cfl.re/48bLI84

The cheapest token does not always mean the cheapest completed task.
Model choice needs a view of task success as well as cost. Join AI at Work, Under Control to explore identity-based budgets, spend attribution, and model-routing trade-offs—without treating estimated savings as guaranteed results.
We’ll show a practical starting point: one application, a governed request path, and a baseline you can review. cfl.re/4iaEtDc

Join Grant Bourzikas, Cloudflare’s CISO, and Daniele Molteni, Director of Product for Application Security, this Thursday, November 12th for practical lessons from the PHP2Shell disclosures. Learn what to check first, how to verify relevant rules are enabled in Block mode, and why teams must prioritize updates while monitoring for potential compromise.
Don't wait for your systems to be tested—register now: cfl.re/4zd4XcA

Cloudflare is distributing the first $301,300 of the Vite Ecosystem Fund to open source projects and maintainers. cfl.re/4iwStY3

Let's explore one potential future for post-quantum privacy on the web, made possible by a recent breakthrough in the design of blind signatures. cfl.re/4feDVdk

Join Grant Bourzikas, Cloudflare’s CISO, and Daniele Molteni, Director of Product for Application Security, on November 12, for a practical discussion grounded in the recent PHP2Shell vulnerabilities. They’ll cover how AI is changing attack and defense, and how teams can combine threat intelligence, WAF managed rules, and timely patching.
Don't wait for the next disclosure—register now! cfl.re/4zd4XcA

November means traffic spikes for e-commerce. How do you load test your infrastructure to prepare for high demand events? #CloudflareChat
AI agents act for millions, but servers see intermediaries that strip user visibility. This post defines the problem space and introduces a collaborative approach to safely identifying, allowing, and managing this automated traffic. cfl.re/3UwbzEA
